01
Asset owner
Approves targets, exclusions and the scan window.
Your team gets clear remediation priorities, an owner for each action and evidence of the retest outcome.
Discuss a pilot at your site ↗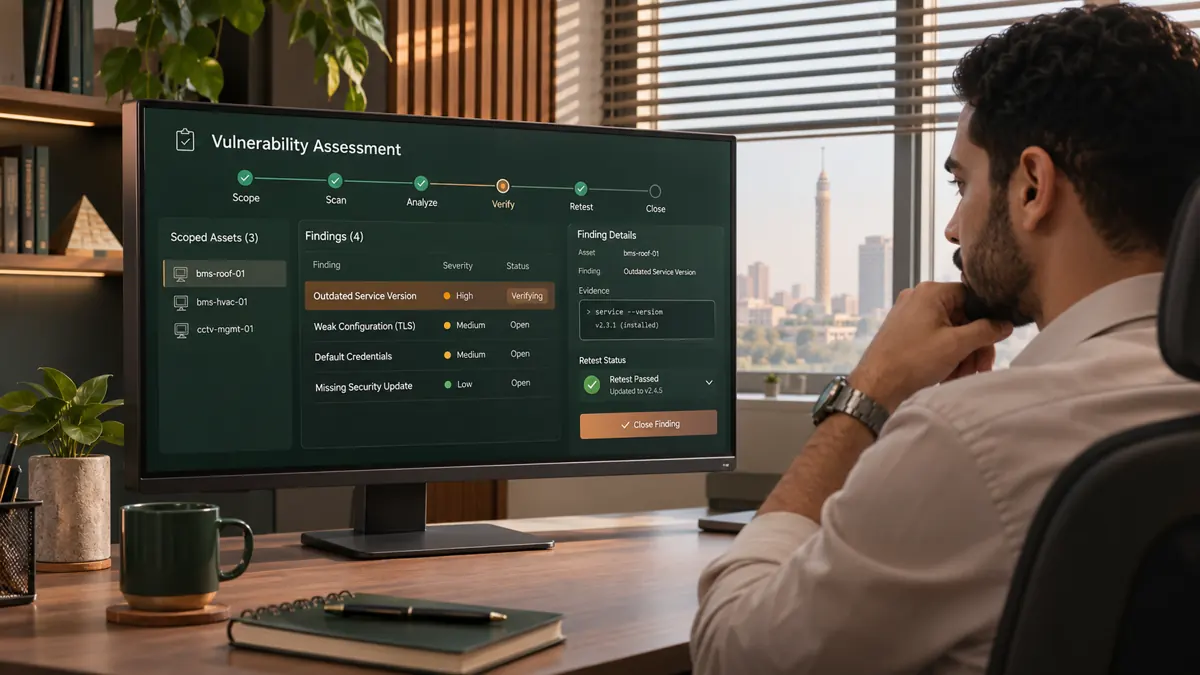
The asset owner approves the target systems, scan window and operating constraints. The authorized scan engine collects evidence from the agreed systems. An analyst validates the finding and sends the recommended action to the asset owner. After the change, we retest and record the outcome and any remaining risk.
The remediation owner implements the agreed fix. The assessment team then verifies the result within the authorized scope.
A managed assessment for one client and a set of assets authorized for testing.
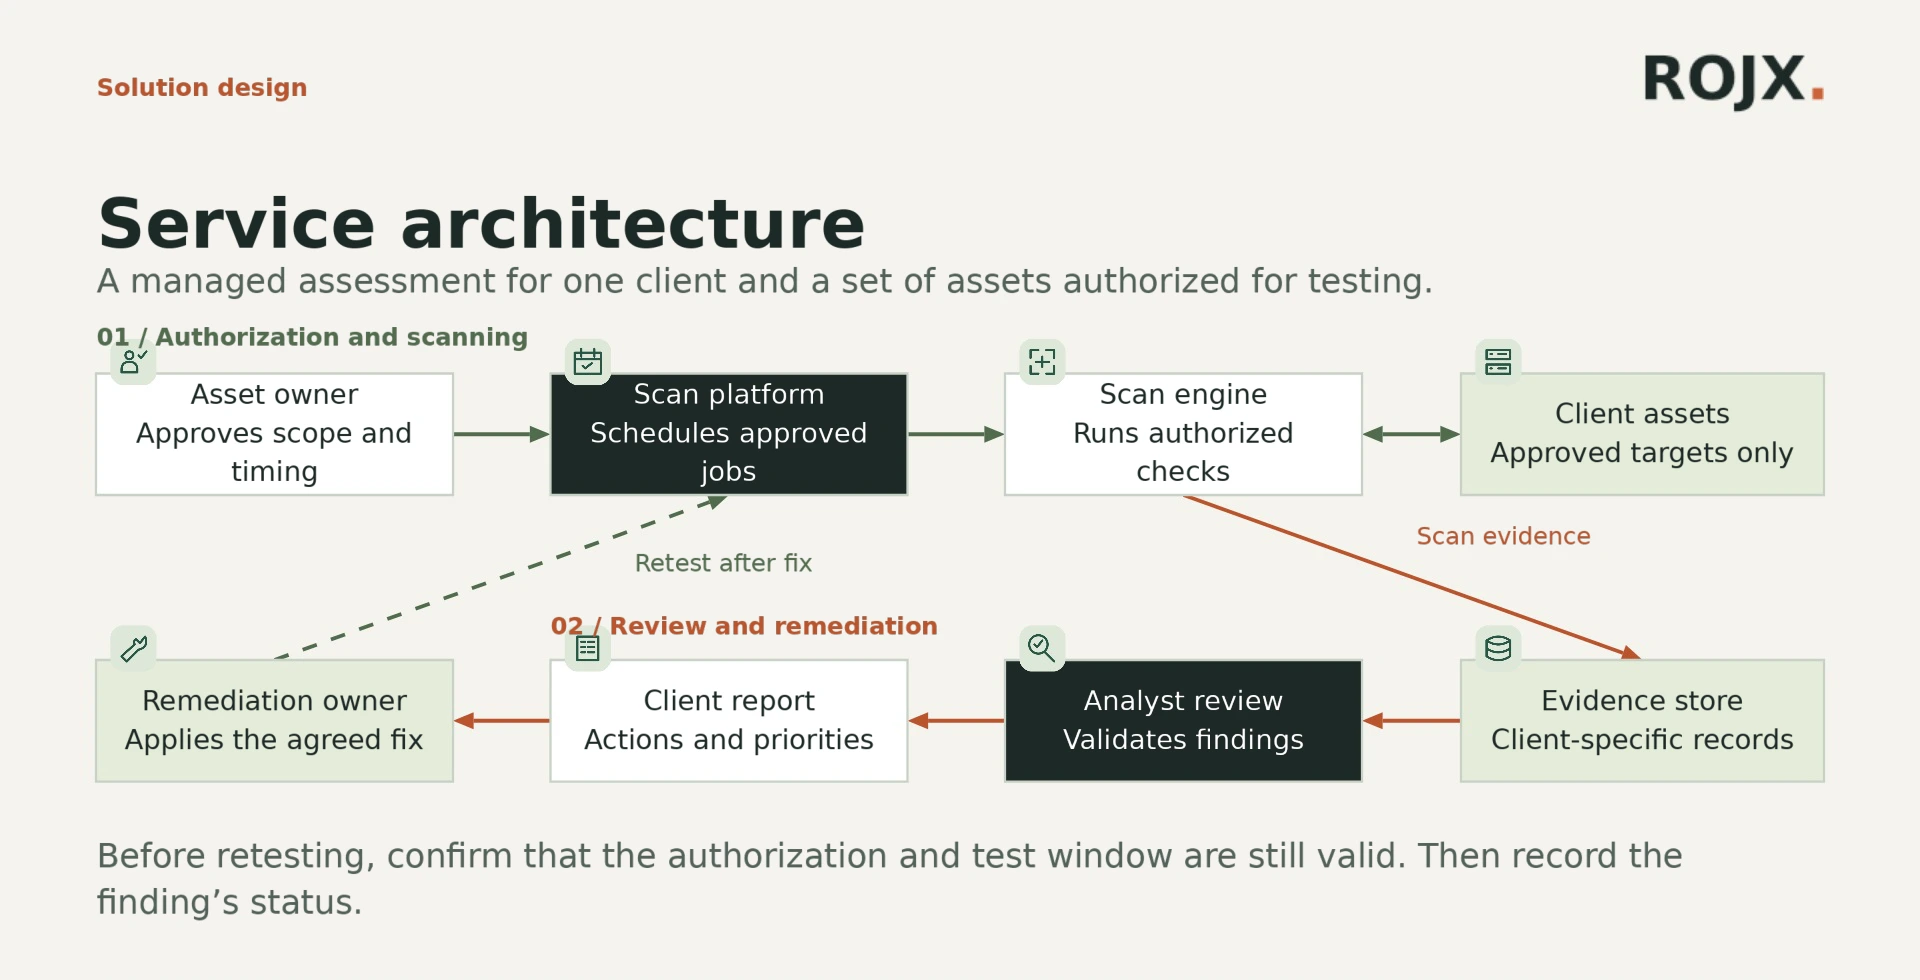
Approves targets, exclusions and the scan window.
Schedules jobs within the approved scope.
Tests authorized assets and collects evidence.
Only systems approved for testing are included.
Restricts access to each client’s evidence.
Validates findings and prioritizes them in the context of the affected asset.
Lists actions, owners and retest outcomes.
Implements the agreed change and requests verification.
Supplies approved credentials for authenticated checks.
Bring a non-sensitive asset inventory and involve the person authorized to approve testing.
Discuss a pilot at your site ↗The asset owner approves targets, exclusions, timing and operational constraints before scanning. Authenticated checks require separate authorization.
The remediation owner applies the fix. The assessment team retests within valid authorization and records whether the issue is resolved, open or needs further review.
An authorized asset owner, address ranges, sensitive systems, a maintenance window and an escalation contact.